-
You bring up a question: why worry about it if the OS is running off a bootable CD? The OS itself can not be corrupted by an external attack.
For a third party to attack from the internet via this avenue, he would have to guess which version of Knoppix is being run, then how the particular user is storing his or her data on which kind of nonvolatile memory. It seems like an awful lot of work, for what?
Similar Threads
-
By tofergregg in forum General Support
Replies: 1
Last Post: 01-09-2005, 06:08 AM
-
By Max in forum Hdd Install / Debian / Apt
Replies: 1
Last Post: 03-10-2004, 06:56 PM
-
By theoldmanschild in forum Hdd Install / Debian / Apt
Replies: 22
Last Post: 02-24-2004, 10:32 PM
-
By massai in forum General Support
Replies: 2
Last Post: 01-01-2004, 11:43 PM
-
By audioaficionado in forum Hdd Install / Debian / Apt
Replies: 1
Last Post: 01-26-2003, 08:38 AM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

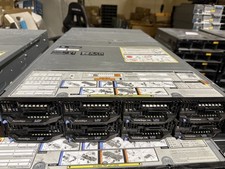
Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99

Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
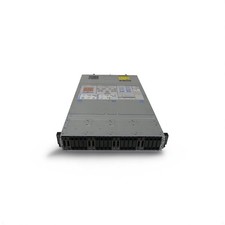
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
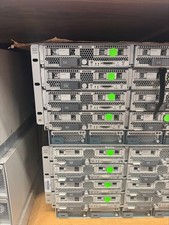
LOT (8) Cisco UCS UCSB-B200-M5 2x6248R 24 core 3.0G 24x64g DDR4-2933 ram
$112000.00
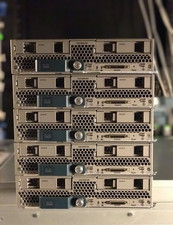
Cisco B200 M3 2x E5-2670V2 10 Core 8x 16GB-128GB Ram Blade Server VIC1240 14900R
$399.00
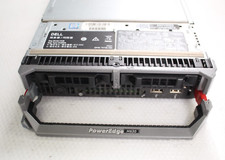
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$96.60
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08



 Reply With Quote