-
Assume that there will be JPEG exploits for Mozilla 1.7.2 . Thus, by running the browser and inavertently looking at an infected site, you will get rooted, and the remote zombie the exploit talks to can read all necessary configuration information. exec( uname -a ) > mail > zombie , for example. The zombie can then select the appropriate rootkit for that version of Linux, and load quite a lot of executable scripts into whatever is writeable - ramdisk, mountable hard disk, operating kernel, whatever. Your hard disk can be scribbled on, your machine can be zombied, passwords and credit cards sent out, all sorts of mischief can be done.
Yes, you can return to status quo with a flick of the power switch - but how does the typical windoze user know when to do that? And it is not quite status quo; your information is on the zombie, and the zombie has put information on your hard disk. If it ever gets control again, it has a running start.
All this can be automated, and there is no protection beyond the read-only nature of the CD, since there is no root password. After the rooting, the CD can be ignored until the next reboot.
The typical Knoppix user is a Linux newbie, straight from windoze. I am giving them a Knoppix CD so they have an alternative to windoze, and most of them will actually use it a long time from now, when their windoze has become unusable, probably by enemy action. I don't want to compound their problems with something that can allow as much damage as windoze itself.
Similar Threads
-
By tofergregg in forum General Support
Replies: 1
Last Post: 01-09-2005, 06:08 AM
-
By Max in forum Hdd Install / Debian / Apt
Replies: 1
Last Post: 03-10-2004, 06:56 PM
-
By theoldmanschild in forum Hdd Install / Debian / Apt
Replies: 22
Last Post: 02-24-2004, 10:32 PM
-
By massai in forum General Support
Replies: 2
Last Post: 01-01-2004, 11:43 PM
-
By audioaficionado in forum Hdd Install / Debian / Apt
Replies: 1
Last Post: 01-26-2003, 08:38 AM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

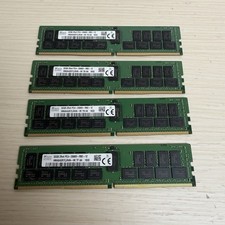
128GB (4x32GB) SK hynix DDR4 PC4-2666V RDIMM ECC Server Ram HMA84GR7CJR4N-VK
$799.00
lOT OF 4 SKhynix 8GB (4 x 8GB =32GB) HMA41GR7MFR8N-TF 2R8 PC4-2133P DDR4 MEMORY
$89.00
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.50
Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
32GB Micron PC4 – 3200AA DDR4 ECC Registered Server RAM - MTA36ASF4G72PZ-3G2J3
$200.00
Windows 11 Pro Install/Recovery/Repair USB Flash Drive
$35.00
Dell Precision 3541 Laptop i5-9300H 2.4GHz 256GB SSD 16GB RAM Win 11 Pro
$189.99



 Reply With Quote