

 Reply With Quote
No such thing as a "hacker proof" server.


Hi, I was hoping someone could help me out on this one. I need to make a server very secure adn I need to close all ports I don't really need. Here is what my server will offer:
WEB PAGE SERVICES (Apache, perl, cgi's)
FTP conectivity
SSH "
DNS
MAIL SERVICE (Using Q-mail, MYSQL)
Now, I need to leave only this ports and services open on my machin, to have it "hacker proof". Anyone know where I can get an easy to understand way to do this? (TUTORIAL with commands etc) I'm new to linux and don't know that much. Thank you.
No such thing as a "hacker proof" server.
I know, I just want to close those ports thanks for the useful help!
http://www.linuxsecurity.com/docs/LDP/Security-HOWTO/
Theres your help
A router would be a good idea. You can even build your own from an old pc and it too can run a Linux distro like Coyote Linux that even has an easy to use web based interface, has great support and is of course FREE!
Personally I use a Linksys WRT54G router (now owned by by Cisco) that runs a Linux kernel but I have built and used Linux routers and learned a great deal in the process.
It really isn't as simple as posting the right commands for you to execute. You're going to have to do some reading and learn aboout networking period.
One very good tool is nmap. Some brief examples:
There are firewalls on Knoppix with easy to use interfaces as well. It really depends on your abilities, your ambition and your budget. You can probably bet on getting flamed anytime you ask such a broad question.Code:nmap localhost nmap 192.168.1.20
Had your post started with "I'm just learning Linux and trying to configure iptables and having a problem with......" You would do alot better. http://google.com/linux is your friend.
Edit
Oh yeah - it sucks when people double post!
This seemed like an interesting question, so I did a little test tonight: I booted my desktop with my newest Knoppix CD. Used all defaults (no cheat codes, default kernel). When Knoppix came up I made sure I was on the network (clicked the links to the websites on the default browser) and then shut down the browser.
I then put another live CD in my notebook and booted that. Ran nmap against my desktop's IP address. With a bunch of scanning this is all I could find:
Open port 68, dhcp client.
Open Port 6000, X11
No other ports were open, and I scanned all 64k, not just the low defaults.
It doesn't seem like there's a lot of vulnerability from the port 68 issue (might help someone on the local lan confuse your system, but ettercap will allow local hacks even without port 6.
Not sure what the port 6000 issues are. Anyone?
My thought remains the same as before the test - assuming you have a high speed connection, use a hardware Home DSL/cable router. Forward only the ports needed to the Knoppix computer (in this case certainly don't forward port 6000 unless you know why). You'll have taken reasonable precautions and be reasonably safe (nothing being completely safe).
I used Nessus to scan my server for vulnerabilities, it detects quite a few, and after that I could take some action to close all doors to intruders.
I also did apt-get install bastille its a really cool program that really hardens your system, if you are not carefull it can REALLY close down your computer, so you have to make sure what do you want to have in your system. In order to run Bastille I also had to do apt-get install perl-tk
 Posting Permissions

OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$145.00
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99
Protectli Vault FW4C-0-8-120 - 4 port, Quad Core, 8GB RAM, 128GB
$180.00

Fortinet FortiGate 60F FG-60F P24286-03-13 Network Firewall Security Appliance
$155.75

OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$248.00
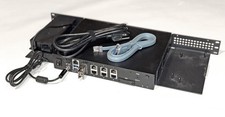
OPNsense Firewall VPN QAT 8-Core Atom C3758 2.20GHz 16GB DDR4 128GB SSD 8xNIC
$175.00
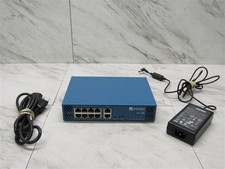
Palo Alto PA-220 Next-Gen Firewall 520-000309-00J
$40.00
Zero Trace Pen: All-in-one Tor Network Anonymous Drive + Cryptocurrency Wallet
$147.00
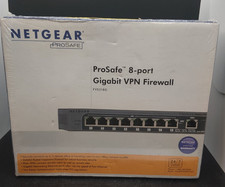
NETGEAR ProSafe 8-Port Gigabit VPN Firewall FVS318G NEW IN BOX
$69.99