-
Senior Member
registered user
thanks for all the help, finally get some idea of how this X security works.
By default, X clients access ~/.Xauthority to find cookies in order to talk to X server.
In order to make scenarios like "su" then run some root only programs "xhost +local:" is needed as this would allow anyone on the same machine(or access to the /tmp/.X11-unix sockets) to connect to the running display.
For a chrooted environment, /tmp in chroot is different from /tmp in hosting so the above won't work. "xhost +localhost" is needed as that means any X apps running on the local machine(not depending on the rootfs anymore) can access the X server.
The above should be good enough for a workstation used by only one person. If one wants more security, it has to resort to using the 'xauth' command to extract the cookies then import into the destination ~/.Xauthority. Though this is still not encrypted in anyway.
If one need to access X apps on another machine, just add "xhost +hostname" but that would mean any X apps from hostname can access the running X server.
hope this will help others.
Similar Threads
-
By Sephiroth? in forum Customising & Remastering
Replies: 1
Last Post: 04-25-2006, 12:55 AM
-
By dvryknopper in forum General Support
Replies: 1
Last Post: 03-31-2006, 05:56 AM
-
By gursharnsingh in forum Customising & Remastering
Replies: 2
Last Post: 01-15-2004, 09:38 PM
-
By rdmelin in forum Customising & Remastering
Replies: 4
Last Post: 08-20-2003, 02:27 PM
-
By sminotti in forum Hdd Install / Debian / Apt
Replies: 2
Last Post: 08-07-2003, 07:46 PM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

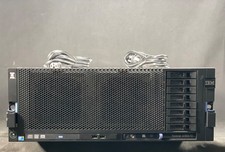
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$149.99

Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
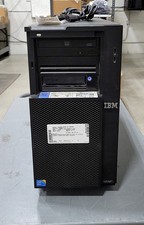
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$108.92
IBM Power S824 12Bay 4U Server - 2x Power8 CPU, 512GB DDR4, MT: 8286-42A
$1731.00
IBM X3650 M5 5462-AC1,2 X E5-2640V3 2.6GHZ 8C, 16 GB, DUAL 750W, 2 X 1TB SERVER
$349.99
IBM SERVER SLED WITH HDD SCSI 8.8GB ,P005043441, AS IS,UNTESTED
$165.00
DELL POWEREDGE HP IBM SERVER XEON GOLD 5415+ 8 CORE PROCESSOR 2.9 GHZ SRMGC
$1299.00
IBM 02AN553 01LL325 IBM I/OADAPTER PCIe / PCN Internal Server Systems Adapter
$199.99


 Reply With Quote