
Is there a firewall in knoppix installed by default? if so where can I take a look at it and if not where can I get one such as ZA that doesn't require manual entry of ACL lists?
Thanks


Is there a firewall in knoppix installed by default? if so where can I take a look at it and if not where can I get one such as ZA that doesn't require manual entry of ACL lists?
Thanks
--If you're installed to HD, ' apt-get install firestarter ' is what I'd recommend. There's some kind of goofy firewall involving a dog somehow on the live-cd, but IIRC it's _caused_ more problems than it has solved.
--Myself, I use a home-brewed iptables script; but I've run into some bugs with it recently after switching to broadband.
Originally Posted by rubic_cube
if all you want to do is browse the net safely you can use this mini-script:
in /home/knoppix create a file called "blockall" and place the following script inside it:
#!/bin/sh
iptables -F
iptables -A INPUT -p all -s 127.0.0.1 -j ACCEPT
iptables -A INPUT -p tcp --syn -j DROP
(==>>note: this is the edited & corrected version of the script! <<==)
then run the following commands:
chmod +x blockall
sudo ./blockall
and that's it. All your ports are closed, you cannot run any server, but you can surf safely.
to reopen everything (to stop this script) simply execute:
iptables -F
HTH
--Have you tried ' nmap'ping a box running that script? There's no DROP rule...
It's ok I'll just play around with iptables some more.
you are absolutely correct. I am sorry about being sloppy. I edited and correted the script in my post above. thanks for pointing this out to everybody
Whenever I try and use the log command nothing happens.
The general iptables -A INPUT -j LOG to log all incoming packets does not generate anything in the syslog file, what do I need to do?
it is my understanding that this script does not allow for any logging. if you want to see how it works, you need to nmap it, or use an online port scanner.
The code logs everything, I can read the log only by doing dmesg syslog, and I can see everything that has been logged, the weird thing is if I try to open syslog any other way it says 0 bytes, so it's empty.
 Posting Permissions


Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Cisco SFP-10G-LR-S Reset & Tested Lot of 2
$32.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99
SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
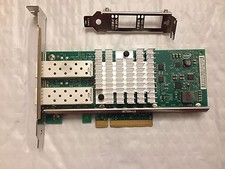
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
Cisco SFP-10G-SR V03 850nm 10GBASE-SR SFP+ MMF 10-2415-03 Transceiver
$4.99
Ubiquiti Unifi USW PRO AGGREGATION 28x10Gbe 4x25Gbe QSFP28 Layer 3 Switch
$700.00

Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99

 Reply With Quote