

 Reply With Quote
I'd say it's pretty much impossible to hack a bootable CD.


How secure is knoppix?
I'd say it's pretty much impossible to hack a bootable CD.
Well....since it is impossible to write to a closed cd I'd say it is the most secure it could possibly be.If you've installed it to your hard drive and set up a firewall you could always scan your ports to find out.
if someone gets root access to your knoppix system, he can then totally destroy your hard drive data or read whatever he wants.
So what's your point that's true with any OS.Originally Posted by neo
If you want TOTAL security you need to not let anyone near the system. If you can acces the machine- you can hack it PERIOD! You should also disable booting from floppy or cd. I really think Bd84 was asking a general security question. Of course we haven't heard back so who knows...
When knoppix is installed, it's just a little less secure than debian by default. ( due to many more programs installed )
But you can increase security by adding firewalls, kernel patches etc.
If you run from the cd on a standalone computer with no harddrive, i'd say that would be pretty damn secure. Just reboot, and you're back to a clean install.
It mainly depends what you mean by "Secure" and what you intend to do with it.
my points being is that the previous two posters seemed to be under the impression that Knoppix because it is on a closed CD is an inpenetrable system. I was merely stating that it is vulnerable as well.
I am under no impression what so ever- I am am absolutely, positively, and unequivocally without a doubt certain that the Knoppix cd itself IS in fact VERY secure. As far as getting in from the outside goes- well are you behind a firewall? You can only be as secure as your firewall. Do you have ports open? There's an avenue and of course that applies to all OS's as well. As eadz mentioned if someone DID get into your machine while you had Knopix booted then just reboot and they're gone. That's the beauty of a ramdisk based Linux router- everything resides in RAM and there is no hard drive to penetrate.
That's the beauty of a ramdisk based Linux router- everything resides in RAM and there is no hard drive to penetrate.[/quote]
Forgive my ignorance, but doesn't your security in this scenario stem partly from the faxt that if you have no read / write storage you don't have anything to steal?
 Posting Permissions

IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99

Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
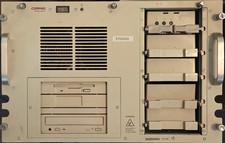
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
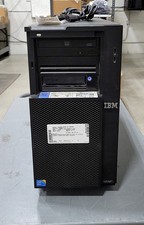
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
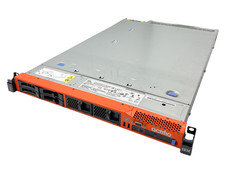
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
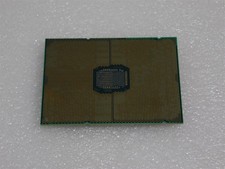
DELL POWEREDGE HP IBM SERVER XEON GOLD 5315Y 8 CORE PROCESSOR 3.2 GHZ SRKXR
$1100.00
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99