-
knoppix.sh autoscan or something better!
I'm relatively new to Knoppix. Long-time linux user, though--primarily Mandrake/Mandriva and recently ubuntu.
I've searched the forums and see that an obvious function must be missing! People have requested, for example, a way to remember boot options/cheatcodes. The advice is change the boot configuration (if starting from a floppy/pen drive, etc.) or remaster. It's not necessarily convenient to do the former because it may necessitate using a floppy+a CD instead of a CD alone. And it's like using a howitzer to kill a fly to remaster for that purpose alone.
What seems to be missing is, just as Knoppix automagically scans and uses swap space, it should have a set path of places to look by default for configuration overrides, cheatcodes, and a post-configuration shell script, perhaps named knoppix.sh or perhaps something more esoteric.
If there is reluctance to have the possibility of data on a questionable disk influence knoppix during boot, then there can be additional cheatcodes to suppress the search behavior, just as there is a noswap option to preserve the potential for forensic analysis of swap partitions.
-
Senior Member
registered user
You should check the "myconf=scan" boot-option. It will scan for knoppix.sh file, and if found will execute it during booting.
This is just the "post-configuration shell script" you are asking for.
You can use this with "KMenu->KNOPPIX->Configure->Save KNOPPIX configuration" to save & reload configuration files.
You can't use this to save boot-options, as that's non-trivial to implement, if it's at all possible.
If you want to use custom boot-options with only the CD, easiest way might be to reburn the CD with edited boot/isolinux/isolinux.cfg file. This way you don't need to do full remaster.
-
Malaire, I suggest you withdraw your post. I made it clear that my complaint is the necessity to use a cheat code to achieve this behavior. Moreover, that still doesn't address the need to affect the boot process without entering stuff every time.
Latest ubuntu will have "Live CD - persistence" to deal with that. The writer argues eloquently: "Keep in mind that not everybody we want to convert to Ubuntu is a power user. I can pretty much guarantee that anything that looks like typing Scary Strings is going to turn people off, not on, no matter how 'powerful' it is behind the scenes."
Here's the wiki doc if you want to see the quote in context: https://wiki.ubuntu.com/LiveCDPersis...t=%28livecd%29
-
Senior Member
registered user
will ubuntu achieve that functionality via multi-session capabilities like puppy linux does? Also, I don't really see why modifying the distro to automatically check for a path for saved cheat codes would really be all that hard, but I think mabe using grub or a modification there of would probably achieve that nicely, I notice that when I start kanotix via grub, there is a text box at the bottom of the screen with all the preconfigured boot options already read in from my hd. If the way grub operates on the live-cd could be modified to check for the values for that text box on a sequential list of possible drives then the user could have persistance on cheat codes at startup without having to enter them in manually, mabe something like this:
How the Proposed Modified Grub Might Work
- Now Checking for usb devices with bootoptions.lst file
scanning for drives marked sd[a-z]*...........
scanning for drives marked ub[a-z]*...........
found bootoptions.lst file @ /mnt/uba1/bootoptions/bootoptions.lst
executing code options
Similar Threads
-
By thierry in forum Ideas
Replies: 0
Last Post: 01-25-2006, 05:48 PM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

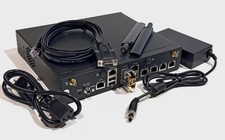
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$145.00
pfSense Firewall 16-Core Atom C3958 8GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI VPN
$184.99

OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$258.00
Check Point 1590 Firewall & w builtin WiFI and builtin LTE sim slot
$95.99

Fortinet FortiGate 60F FG-60F UTM UTP License Until 2027 Network Security FW VPN
$229.99
Fortinet FortiGate 80E 12 Ports Firewall Appliance
$20.25
Protectli Firewall VP2440 – 2x 10GbE, 2x 2.5G
$500.00
OPNsense Firewall VPN QAT 8-Core Atom C3758 2.20GHz 16GB DDR4 128GB SSD 8xNIC
$175.00
Zero Trace Pen: All-in-one Tor Network Anonymous Drive + Cryptocurrency Wallet
$147.00
Fortinet FortiGate FG-40F Network Security Firewall NO RACK EARS
$49.99



 Reply With Quote