-
Trojan vulnerabilities
ok - I'd like to clarify my interest in this thread - does KNOPPIX secure all its ports out of the box?
I would like to introduce KNOPPIX as a secure alternative to WinXP out of the box.
I booted KNOPPIX 5.0.1 and ran a Trojan scan at http://scan.sygate.com. It reports the following vulnerabilities:
Trojan 21 OPEN Back Construction, Blade Runner, Doly Trojan, Fore, FTP trojan, Invisible FTP, Larva, WebEx, WinCrash
Trojan 23 OPEN Tiny Telnet Server (= TTS)
Trojan 80 OPEN Executor, RingZero
I was a bit surprised to see this. Are there additional steps I need to take to secure my PC?
Is there a reason these ports are open by default?
Similar Threads
-
By tbr.yel in forum Networking
Replies: 0
Last Post: 01-23-2007, 11:37 AM
-
By django in forum Networking
Replies: 16
Last Post: 08-07-2006, 09:27 PM
-
By eq2675 in forum General Support
Replies: 1
Last Post: 06-07-2005, 03:54 AM
-
By sakiZ in forum General Support
Replies: 3
Last Post: 02-14-2005, 02:28 AM
-
By kievlak in forum General Support
Replies: 1
Last Post: 11-13-2004, 07:12 PM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$140.00
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
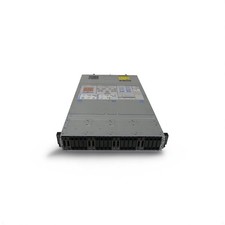
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
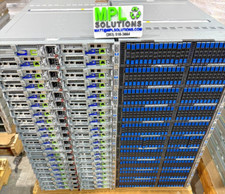
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
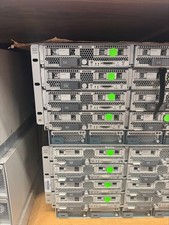
LOT (8) Cisco UCS UCSB-B200-M5 2x6248R 24 core 3.0G 24x64g DDR4-2933 ram
$112000.00
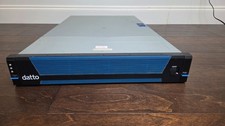
Datto S3E12000 RACK SERVER 2U 2x Xeon E5-2670 v3 2.30GHz 32GB RAM 2x PSU 14 BAY
$399.95

Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08



 Reply With Quote