Yeah right, of course not.
I just finished reading an article which describes, among other things, that a router's firewall might be manipulated (reprogrammed) and deactivated by means of CrossSiteRequestForgery.


Yeah right, of course not.
I just finished reading an article which describes, among other things, that a router's firewall might be manipulated (reprogrammed) and deactivated by means of CrossSiteRequestForgery.
 Posting Permissions

Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
INTEL CORE I5-11600 2.80GHZ PROCESSOR | SRKNW
$109.99
INTEL CORE I7-870 SLBJG 2.93GHZ LGA1156 4 CORE CPU PROCESSOR
$23.00

Lot of 2 INTEL CORE ULTRA 5 245 PROCESSOR | 3.50 GHZ | SRVFE
$256.99
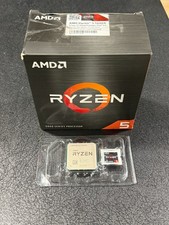
AMD Ryzen 5 5600X Desktop Processor (3.7GHz, 6 Cores, AM4 CPU) 100-100000065
$135.00
Intel Core i9-9900 3.10GHz CPU Processor SRG18
$165.00
Intel Core i7-9700 3.00 GHz LGA 1151 Desktop CPU Processor SRG13
$79.99

Intel Core i5-7500 Processor (3.4 GHz, 4 Cores, LGA 1151) - SR335
$12.99

Intel Core i5-12600 SRL5T 12th Gen Desktop Processor 3.30GHz LGA1700 CPU
$185.00
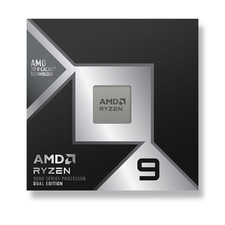
*Brand New-Sealed* AMD Ryzen 9 9950X3D2 Dual Ed. 4.3GHz 16Core AM5 (Bulk+Fast)
$790.00

 Reply With Quote