-
There is one big name company that is always listed on my http connections, they have 4 primary servers - and can hop to others if you block theirs. They can disrupt me but with an active firewall, the moment they try any I/O they get dropped. They used to trace my http back, and then begin searching for open ports using about 10 to 20 different connections from the same server, and tie up all my resources. This might not make scientific sense, but it does happen.The syn floods have stopped as well. Some time nusiance seems the objective - for me. But I am certain ther are cataloguing and planting bots for all those happy-go-lucky users without a care.
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

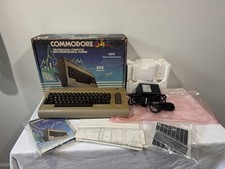
1980's Commodore 64 Computer with Original Box and Manuals
$80.00
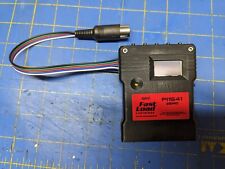
Pi1541 Zero with Epyx Fastload Hat, Case & 16gb SD for Commodore 64 and 128
$79.99
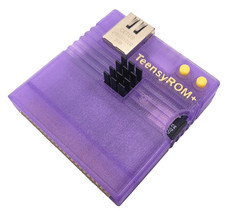
TeensyROM+ TR+ v0.4 Cartridge for C64/128 - w/ Case & 32GB SD Preloaded
$89.50

Commodore 64 Dead Test & Diagnostic Cartridge & Test Harness Set - USA seller
$39.99
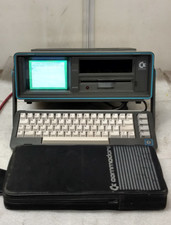
Commodore SX-64 Personal Computer
$600.00

Commodore 1541 Emulator PI1541 HAT with ROTARY, OLED screen, USA Seller
$29.99

Commodore 64 Serial Cable 6PIN DIN 1541 1571 C64 128 C128 Disk Drive Printer USA
$10.49
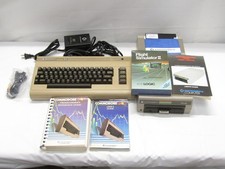
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
Commodore OS USB | Bootable LIVE + Install | The Ultimate Gaming Linux OS | NEW
$11.99
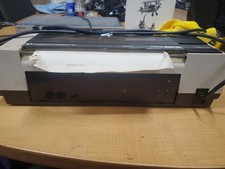
RARE Commodore MPS801 Printer - 1st printer for the 64 - powers on
$70.00



 Reply With Quote