-
In a CD/DVD-oriented distro like Knoppix, the CW says it makes no sense to password protect users (root or otherwise). In the case of a HD/flash-installed implementation with persistent store, it makes more sense to protect the KNOPPIX-DATA file. That way, anyone (e.g. the kids) can boot to the base system without a password, but all the goodies in the changeable system are protected from changes/prying. Knoppix is set up to make it easy to poke around and (potentially) mess things up, but not permanently. So, the sudo command gives virtually anyone unlimited power over everything not encrypted, until the next boot.
Cheers!
Krishna 
p.s. I split this off from the prior thread from 2004/2005, as it seemed confusing to have them both together despite major changes in the distro (e.g. persistent store.)
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

Samsung 256GB SSD MZ-JPV256S/0A2 PCIe Solid State Drive SSD SSUBX 655-1959A
$22.02

Samsung T7 Shield 1TB Portable External SSD USB 3.2 Black MU-PE1T0S NEW SEALED
$219.99

Samsung Galaxy Tab S10+ 5G (256GB, 12GB, Wi-Fi + Cellular, Unlocked) 12.4" X828U
$579.99
Samsung Galaxy Tab Active 3 / 64 gig/ WIFI/ IP68 Rated
$85.00
RAM-GDS-SKIN-SAM80-NG RAM IntelliSkin® Next Gen for Samsung Tab A7 Lite 8.7”
$82.99
3 -M.2 2280 512GB SSD - Samsung MZNTE512HMJH, MZNLN512HMJP, Toshiba KSG60ZMV512G
$155.00

RAM-GDS-DOCK-SAM80CPU RAM GDS® Tough-Dock™ for Samsung Tab A7 Lite 8.7"
$159.49
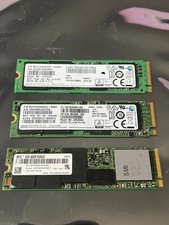
1 lot of 3 (2)Samsung PM951 SM961 & (1)Intel SSD 600P 256GB M.2 2280 SSD NVMe
$109.00
Samsung Galaxy View Tablet 18.4 SM-T670/677A Digitizer 100% Original Oem
$152.99
Original for Samsung NP950QCG-K01US LCD Screen Touch Full Top Assembly FHD Blue
$299.00


 Reply With Quote