-
Senior Member
registered user

Originally Posted by
utu

I have two concerns with the initial premise here.
Unless your Knoppix user is denied root privileges,
making that partition which contains /mnt-system read-only on a write-able
medium offers no real protection against unauthorized changes to the contents
of /mnt-system.
If the Knoppix user is denied root privileges completely,
there are many useful things his Knoppix can't do.
I'd like to see how changes to init might get around these considerations.
Even if it is possible to remount /mnt-system rw, having it mounted ro by default is clearly a safety measure. And, for example, everything could be placed in loop-mounted ISO images. So that you have to re-create it each time you want to update your persistent store. This could be equivalent to using one or more cloop/squashfs overlays.
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Cisco Meraki MA-SFP-1GB-SX Network Tranceiver Module
$89.00

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
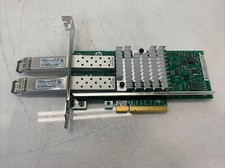
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
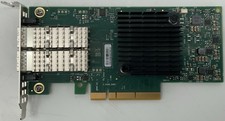
Dell Mellanox ConnectX-4 Lx CX4121C Dual 25GbE SFP28 LP | 20NJD
$25.00

HPE 560SFP 2x 10Gb SFP+ PCIe Both Profile Network Card 669279-001 665247-001
$14.90
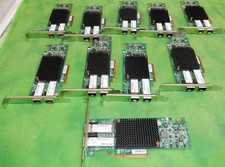
HP 557SFP+ ETHERNET 10GB 2 PORT 792834-001 788991-001 HIGH LOT OF 10
$70.00
Lot of 8 Mellanox MAM1Q00A-QSA Rev B3 QSFP+-to-SFP+ 40G/10G Adapter Transceiver
$69.97


 Reply With Quote