
 Reply With Quote
why do you make so hard properly formatting a message? Why can't poster not enter plain html?


there actually is a way to boot from an iso knoppix image which is mounted read-only (ro), namely: using the "forensic" startup option. You would, say, startup with the one liner:then on init 2 you go:boot: knoppix64 no3d init 2 forensic bootfrom="/dev/sd"to get:mount | grep sdThe problem with the "forensic" option is that then all other partitions are mounted write-protected, read-only. Or, how do you work around this? There should be a "bootrofrom= ..." option for those of us who want to make sure the knoppix baseline is not being altered and want to be able to easily check if that is the case. On init 2 you could always edit /etc/passwd in order to create and change user directories Since the Internet has become such a promiscuous environment in which "Russian hackers" are constantly messing for fun and profit every connected device, introducing such a startup option would be great. I don’t believe at all in antivirus software It shouldn’t be that hard. Probably just including menuentries in the grub2 loader? What may I be missing? lbrtchx/dev/sd on /mnt-iso type ext4 (ro,relatime,block_validity,delalloc,barrier,user_ xattr,acl)
why do you make so hard properly formatting a message? Why can't poster not enter plain html?
after noticing the corrupted formatting but I can't edit it at all
I normally use the "forensic" option with a pendrive. But what I do is keeping some files/folders (new versions of tor browser, firefox and libflashplayer.so, checked with the sum when downloaded) zipped and encrypted in some folder inside my Knoppix with gpg (gpg -c --cipher-algo AES256 file.zip). So, I boot with knoppix forensic, write my wifi password and then decrypt those files (gpg file.gpg), remember that home folder is not read-only in that session. Every time I boot all is clean. The problem could be if my home folder (and so, my browsers and files) are hacked/cracked in that session. I avoid scripts (noscript addon) and normally I only use the browser, only some times flashplayer (yes, that´s dangerous), but if I want I can delete all the decrypted files and encrypt them again in that session. But it´s great to know that in the next boot (or if I begin the process again in the current session) all is always clean.
Last edited by joselb; 12-23-2016 at 07:41 AM.
well, yeah I also:
1) make the image file read-only
2) make their attributes unmodifiable (lsattr chattr)
3) resize the file system to its bare minimum (using gpated)
but a boot ro from an image would be a great option
I don't understand it very well, even if you boot from an image, using forensic option it will be read only, but it's impossible to use knoppix if ALL is read-only, some parts won't be that way. But the system part will remain read-only and protected in every boot. Maybe I miss something here.
The OP seems to enjoy his trolling.
http://knoppix.net/forum/faq.php?faq...eading_postingOriginally Posted by philo

 Posting Permissions


Intel Xeon E5-2680 V2 2.8GHz 10-Core 25MB 8GT/s SR1A6 LGA2011 B Grade Server CPU
$7.95
HPE DL360 G10 CTO Server W/ 2x800W 1x LP PCIE RISER 1xFLEXROM 2XHIGH PERF FANS
$200.00
NEW HP Z4 G4 Workstation Xeon W-2123 16GB ECC 256GB NVMe NVIDIA T400 750W Win11
$450.00
HP Z420 Tower Workstation Xeon E5-1620 3.60GHz, 4GB Ram, NO HDD, NO OS
$140.00
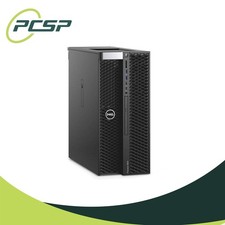
Dell Precision T5820 Workstation 3.70GHz W-2135 No RAM/ GPU/ HDD/ OS
$179.98
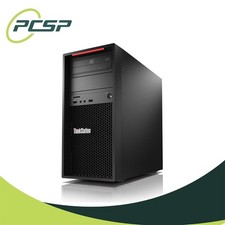
Lenovo ThinkStation P520c Intel Xeon W-2133 6-Core 3.60GHz -NO RAM/ HDD/ GPU/ OS
$127.54
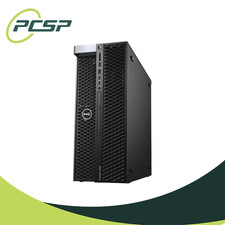
Dell Precision T7820 2x Xeon Gold 6130 2.10GHz 950W No RAM GPU HDD 4x SATA
$374.48
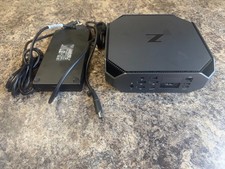
HP Z2 Mini G5 Workstation Xeon W-1270P 3.8GHz/16GB/1TB SSD/ NVIDIA T1000/W11 Pro
$349.00
DELL Precision T3420 | Xeon 1240v6 | 525GB SSD |16GB RAM |Nvidia GPU |Win11
$149.00
Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00