

 Reply With Quote
Try /sbin/iptables -A INPUT -p tcp --dport 68 -j DROP a good tutorial and sample script are here and there are a couple of other firewalls available such as Guarddog and Bastille-Linux in Debian.Originally Posted by /Knoppix/Knewbie/


hi just got knoppix, and need a little help getting my firewall in to stealth mode on www.grc.com
{its fine at sygate sos}
but at gibson it shows port 68 is open and port 67 is closed and all the other ports are in stealth mode..
i installed firestarter which didn't seem to do much so i then used this line
/sbin/iptables -A INPUT -p tcp --syn -j DROP
which put all but two ports in to stealth mode
any advice on how to stealth these 2 ports ??
cheers
/Knoppix/Knewbie/
Try /sbin/iptables -A INPUT -p tcp --dport 68 -j DROP a good tutorial and sample script are here and there are a couple of other firewalls available such as Guarddog and Bastille-Linux in Debian.
--Also try ' nmap localhost ' and ' less /etc/services ' to see which programs run on those ports. You can also use ' lsof |grep 68 ' to list open files/ports.
--I'm concerned if you disable port 68 (bootpc) your DHCP server will stop working, but I don't know that much about DHCP or firewalling.
(COMPLETE IPTABLES NEWBIE QUESTION) - After skimming thru the iptables tutorial and understanding about 2% of it, what about limiting your DROP rule to interface ppp0?
i have tried going to the sites you reccommend but they seem not to be functioning/
o well cheers for the advice anyway
woody
Here is the Guarddog and Bastille-Linux web sites I just checked them and they both work from my machine another place you can try is Arno's Iptables which is what I use it's fairly easy to setup you only have to edit a couple of lines in the script(s) and change some permissions on the files and you are ready to use it.
Most firewalls that I have seen do that when you are setting up the rules you have your external (internet) connection which is what you would be dropping the incoming packets on you can still establish outgoing connections to get what you require from the external interface unless you go out of your way to block outgoing connections on the ports. If you have an internal interface that you are using NAT on to share the connection it is usually on a trusted internal interface so you can have access to your internal network. This is what I do with my firewall machine from the outside my computer does not exist on the internet if you scan it but on the internal side my firewall machine runs only SSH so I can get to it to check for upgrades to my Woody (actually Mini-Woody now known as Bonzai Linux) install on it and HTTP so I can serve myself some web pages that I have.
 Posting Permissions

Apple Mac Pro 2019 1TB OEM SSD Kit-832GB +128GB - 656-0122/ 656-0121
$69.99
Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$60.00
Dell Latitude 14" Laptop Computer Intel i5 Up To 32GB RAM 1TB SSD Windows 11 Pro
$545.25
External SSD 1TB 2TB 4TB Portable Hard Drive USB 3.0 Type-C High Speed PC Mac
$19.99
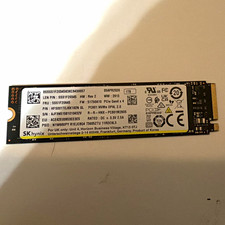
SK hynix PC801 1TB M.2 NVMe PCIe Gen4 x4 Internal SSD HFS512GDE9X081N
$90.00

SAMSUNG T7 Portable SSD 1TB Indigo Blue USB 3.2 Gen2 External MU-PC1T0H/AM
$159.99
1TB Kingston DataTraveler Max DTMAX/1TB USB Type-C Flash Drive
$86.95
Acer Predator Helios Neo 16S AI 16" i9 275HX 2S RTX 5070 Ti 32GB 1TB SSD Refurb
$1746.47
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
fanxiang S660 1TB PCIe 4.0 NVMe M.2 2280 Internal SSD w/ Heatsink Gray
$120.00