

I thought I would use knoppix 3.2 as a protocol analyzer. I can boot up just fine without any issues. I have my switch setup to port mirror. After I bring up a console in KDE and type: tcpdump about a million packets go flying by the screen so I know that my network card is seeing all traffic. As soon as I try to filter these packets with a command such as: tcpdump -i eth0 host 192.168.1.1 using an actual ip address that I know traffic is going to and from, I don't see anything. I've checked the tcpdump manual but it is as if any expression that is added to the end of tcpdump seems to kill it's ability to see any traffic. Has anyone seen this problem or can confirm that I'm not doing something wrong? I am in the process of getting the latest 3.3 9-24-03 version to see if this makes any difference. I've also tried Ethereal under KDE and as long as I just capture anything to the port everything is seen but when trying to use a filter to limit what's captured it fails also.
thanks in advance,
 Posting Permissions

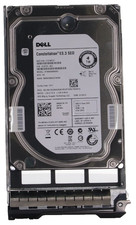
Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
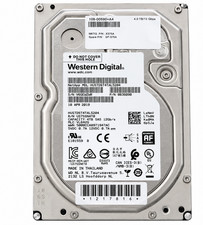
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00
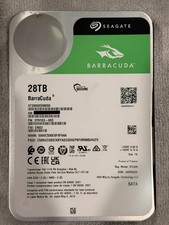
Seagate BarraCuda 28TB 7.2K SATA 6Gb/s 3.5in Internal HDD ST28000DM000 - Tested
$670.00
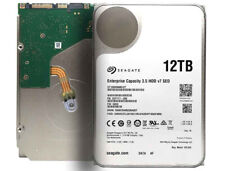
Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
Seagate ST4000NM0034 Enterprise 4TB 7200RPM SAS 12Gb/s HDD v4
$39.00
Seagate ST500DM009 BarraCuda 500 GB 3.5" SATA III Desktop Hard Drive
$14.99
HGST HUS724040ALA640 HDD 4TB SATA 6Gb/s 7.5K 3.5" 0F19459 512 b/s
$78.00
Toshiba 14TB MG07 MG07ACA14TEY 7.2K RPM SATA 6Gb/s 512e 3.5" Enterprise HDD
$329.00

DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95

Seagate ST8000NM0075 Enterprise Capacity 3.5 HDD 8TB SAS Hard Drive 8TB EXOS
$184.99


 Reply With Quote