
 Reply With Quote
don't you have to start *dm instead of starting X?


I am really happy with my customization but now am blocked: I have to enable kdm or xdm to control the access.
It works in chrooted environment but not on the burned image.
Tried to launch kdm in /etc/init.d/xsession (after X is started) but with no success (nor with xdm)
Any help by you gurus would be really appreciated.
Knoppix is GREAT !
don't you have to start *dm instead of starting X?
I thought about this but what about the detection of the accurate X server ?
I think I also have to play with pam config but I am a little bit lost ....
imho it isn't a big problem, just change XFree86 in kdm in xsession. you may have to remove some of the parameters though. Detection isnt done in xsession, it copies XF86Config-4 to /etc/X11/ in knoppix-autoconfig
Ok but it seems that there's some (re)probing in xsession.
I can't figure where I should start *dm and how the process could go on after (but it must also be because of my lack of knowledge in Linux)
simply put /etc/init.d/xdm start in your inittab.
then be sure to copy /etc/X11/XF86config-4 to your chrooted X11.
it works fine, i did some days ago
good luck
 Posting Permissions

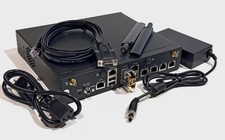
OPNsense pfSense 8-Core Atom C3758 2.2GHz 8GB DDR4 64GB SSD 8x NIC QAT AES VPN
$145.00
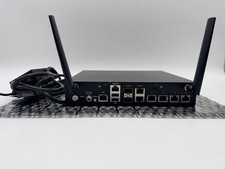
OPNsense Firewall 16-Core Atom C3958 16GB DDR4 RAM 64GB SSD 8x 1Gbe QAT AES-NI
$195.00
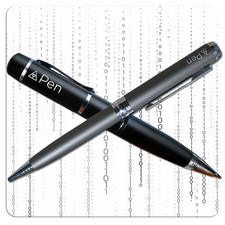
Zero Trace Pen: All-in-one Tor Network Anonymous Drive + Cryptocurrency Wallet
$147.00
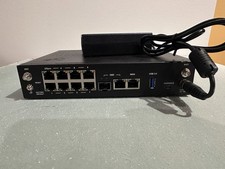
Check Point 1590 Firewall & w builtin WiFI and builtin LTE sim slot
$95.99
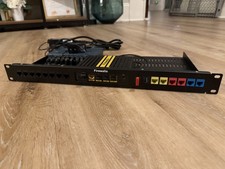
Firewalla Gold Plus 2.5GbE Firewall Router with Rack Mount - Excellent Condition
$600.00

Fortinet FortiGate 60F FG-60F UTM UTP License Until 2027 Network Security FW VPN
$69.99

OPNsense pfSense 16-Core Atom C3958 16GB ECC RAM 512GB SSD 8-Port QAT AES-NI VPN
$258.00
Fortinet FortiGate 60F FG-60F Firewall Tested Reset Deregistered OEM PSU
$99.99
$170.00
SonicWall TZ280 Firewall 03-SSC-6933 Advanced Edition 3YR NEW SEALED
$999.99