
This post is getting very few responses although it looks serious. Any response from Stephen,Rickenbacherus,etc ? I am really concerned about this.


This post is getting very few responses although it looks serious. Any response from Stephen,Rickenbacherus,etc ? I am really concerned about this.
No-one has sent it to the debian-knoppix mailing list, however, it is a local exploit.
Now if you're worried about a local exploit, I take it you have your computer in a locked safe with no physical access to it?
Additionally, I don't see a .qt directory in /tmp/ . Do you have one?
What is a Local Exploit?
It means you must already have an account on your computer before you can exploit it.
So does it mean this security problem is not severe?
Please make this clear.
Thanks!
I think the post got the response it deserved I have the last two version installed on a spare drive I use for testing and could find no such file in either.
And to be perfectly clear on the local expliot a person must have physical access to your machine and be able to login to the computer. The only totaly secure computer is one kept under lock and key that only you have access to and with no connection to any network.
I was concerned because I do have those files both on root's home and my home-the is the .qt directory with the files mentioned in that alert. I have version 0606.
Would it be safe to delete the directory? I have no idea if it relates to the qt programs.
I've logged into my nephew's computer which I have put the 06-06 version on a well and the file is not here either that being said it is only a directory in the /tmp directory so remove it if you feel that uncomfortable with it being there as was stated above the only way someone could use the exploit ( if it is actually one this has yet to be confirmed) would be to have access to your computer.
Thanks Stephen for replying and please pardon my seemingly paranoid reaction to this. One of the reasons why I am shifting to Linux is the frequent security problems and various viri which seem to plague windows systems. At one time my pc and the office pc was infected with 10 viri which fortunately norton was able to catch. And now this.
BTW, the .qt directory in my pc is NOT in the /tmp. It is one of the hidden directory on the /home/user. In this case, does this relate to the alert or it is not affected ,being not in the /tmp directory?
The .qt files in the other directories are fine and safe. Don't remove them!
If you're still feeling paranoid (and it's not such a bad thing!) you might like to install a firewall and look for Linux security articles on the internet (Google will chuck up plenty).
But it's worth mentioning that the best security strategy is to simply back up your data.
 Posting Permissions

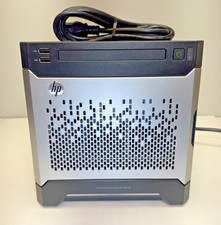
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
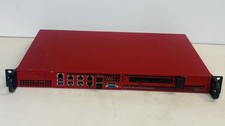
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
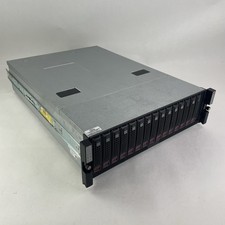
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
$280.00
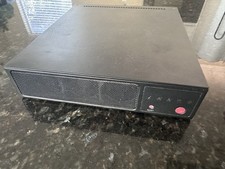
Supermicro E200-8D Mini Server Xeon D-1528 6-Core 64GB ECC 1TB SSD 2x10GbE IPMI
$525.00
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
SUPERMICRO CSE-836 XEON E5-1620 v3 @ 3.50GHz, 32GB RAM, NO HDD/OS
$299.99
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$187.50
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99

 Reply With Quote