-
Senior Member
registered user

Originally Posted by
Bukowski
That has to be the worst piece of advice I've ever seen offered. If you're online you're going to get scanned. And you're in just as much danger with Linux as Windows, I can see you've never had to secure a server. Lets take a quick look at a default Knoppix HDD installation with nmap:
Well if you are going to give advice at least be truthful about it. Those ports are not open after an install you have upgraded the install without removing the servers and they have been started you because you have accepted the default Debian scripts instead of keeping the Knoppix ones.
Similar Threads
-
By eadz in forum Hdd Install / Debian / Apt
Replies: 11
Last Post: 11-04-2010, 09:02 PM
-
By NetKatz in forum Hdd Install / Debian / Apt
Replies: 2
Last Post: 05-02-2004, 02:38 PM
-
By pierrevn in forum General Support
Replies: 5
Last Post: 12-12-2003, 07:34 AM
-
By Edix in forum Hdd Install / Debian / Apt
Replies: 1
Last Post: 11-10-2003, 08:20 PM
-
By kipizit in forum General Support
Replies: 1
Last Post: 11-07-2003, 03:08 AM
 Posting Permissions
- You may not post new threads
- You may not post replies
- You may not post attachments
- You may not edit your posts
-
Forum Rules


Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$119.99
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
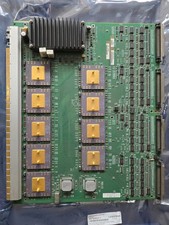
Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$749.99
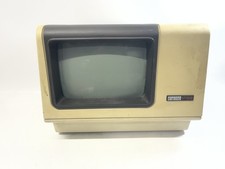
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
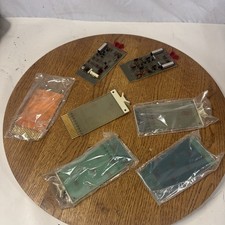
Vintage DEC Digital Equipment Flip-Chip Module Lot Parts
$59.99
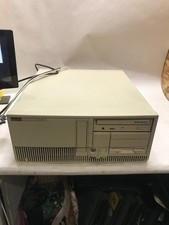
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00



 Reply With Quote